For MSPs, MSSPs and SOC teams

One queue for every alarm, for every customer.

Signum is a security operations platform. Alarms from your SIEM, EDR, firewalls and mail security land in one place, each customer or business unit stays in its own tenant, and your analysts take every case from triage to a closed incident and a monthly report.

One tenant per customer Self-hosted SSO and role-based access
Who it is for

One platform, two ways to run it

Signum works the same whether you defend your own company or dozens of customers. The only difference is how many tenants you create.

MSPs & MSSPs

Serve many customers from one console

Your analysts work in a single queue while every customer's data, users and integrations stay separate.

  • One tenant per customer, with its own sources, users and playbooks.
  • Analysts see only their customers. Assign each person exactly the tenants they cover.
  • A monthly PDF per customer with response times, top sources and incident timelines.
  • Customer logins if you want them, read-only or tenant admin, with SSO per tenant.
Typical setup: one tenant per customer, analysts shared across tenants
In-house SOC teams

One queue for the whole organization

Stop switching between the consoles of your security tools. Work every alarm, incident and response from one place.

  • Every tool feeds one queue, with related alerts folded into unified alarms.
  • Incidents with a history: assignment, notes, status and everything that led to them.
  • Playbooks so routine response runs the same way every time.
  • Tenants for subsidiaries or business units, if you have them. A single tenant if you do not.
Typical setup: one tenant, or one per business unit, SSO from your identity provider
Works with the tools you already run
SIEM EDR & XDR NDR Network monitoring Perimeter & firewalls Email security Threat intel feeds Identity & SSO Ticketing & ITSM AI engines REST API & webhooks
The product

See what your analysts work with

Screenshots of Signum running with sample data.

01

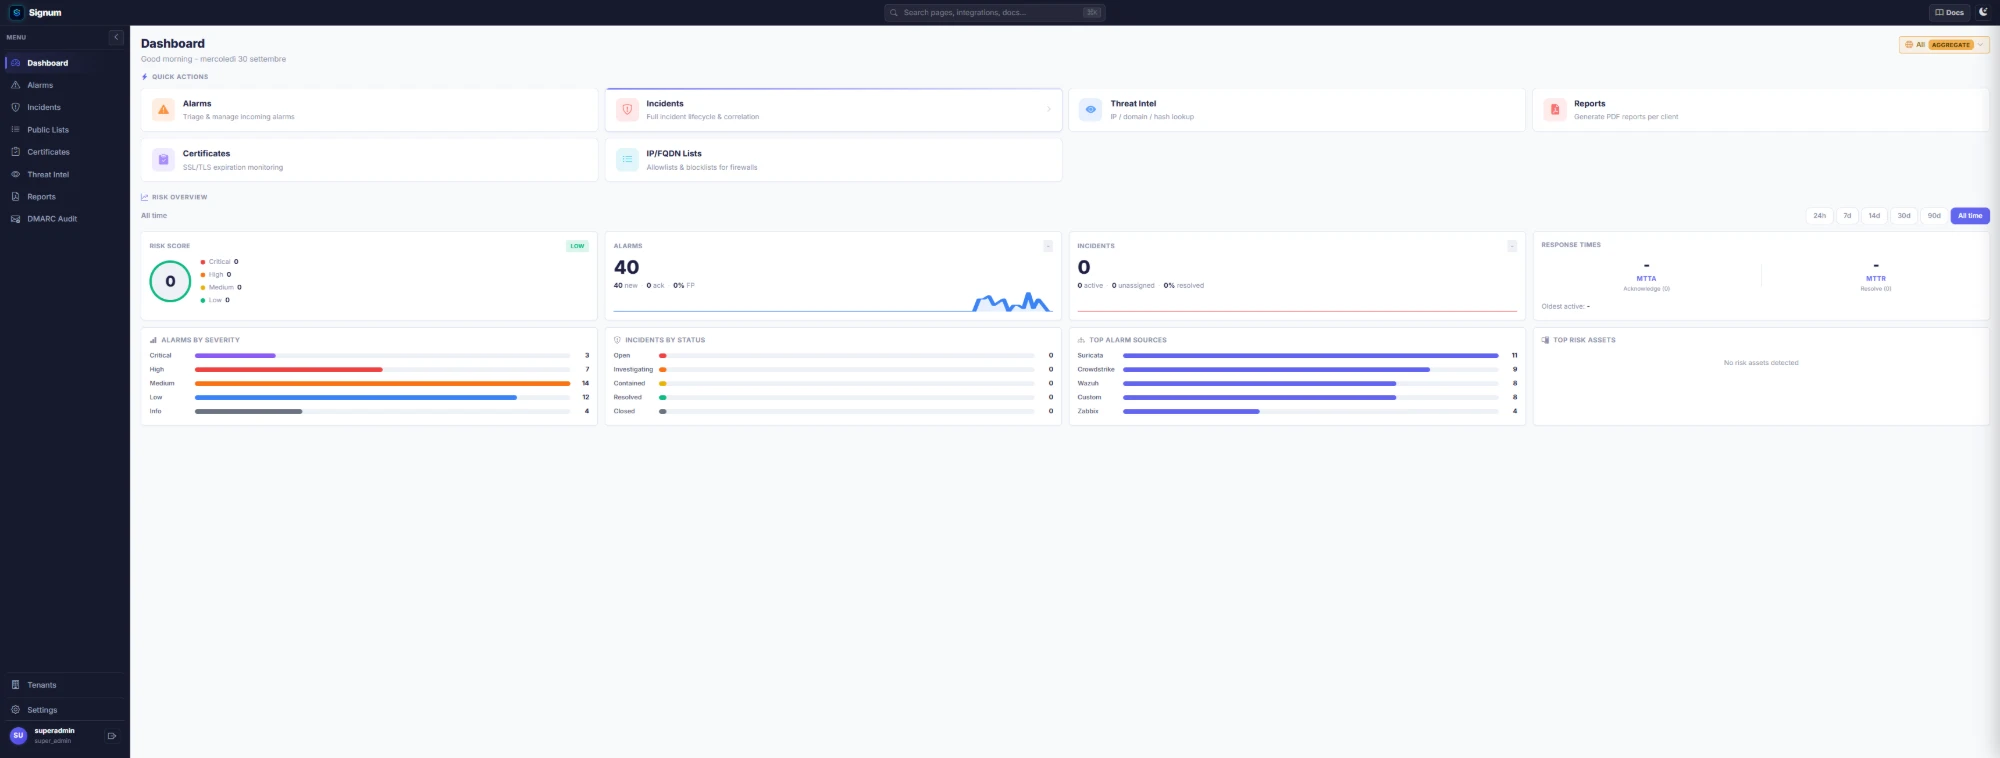
The state of the SOC in one view

Risk score, alarm and incident counts, response times and top alarm sources for the period you choose, from the last 24 hours to all time.

Signum dashboard with risk score, alarms, incidents and response times
02

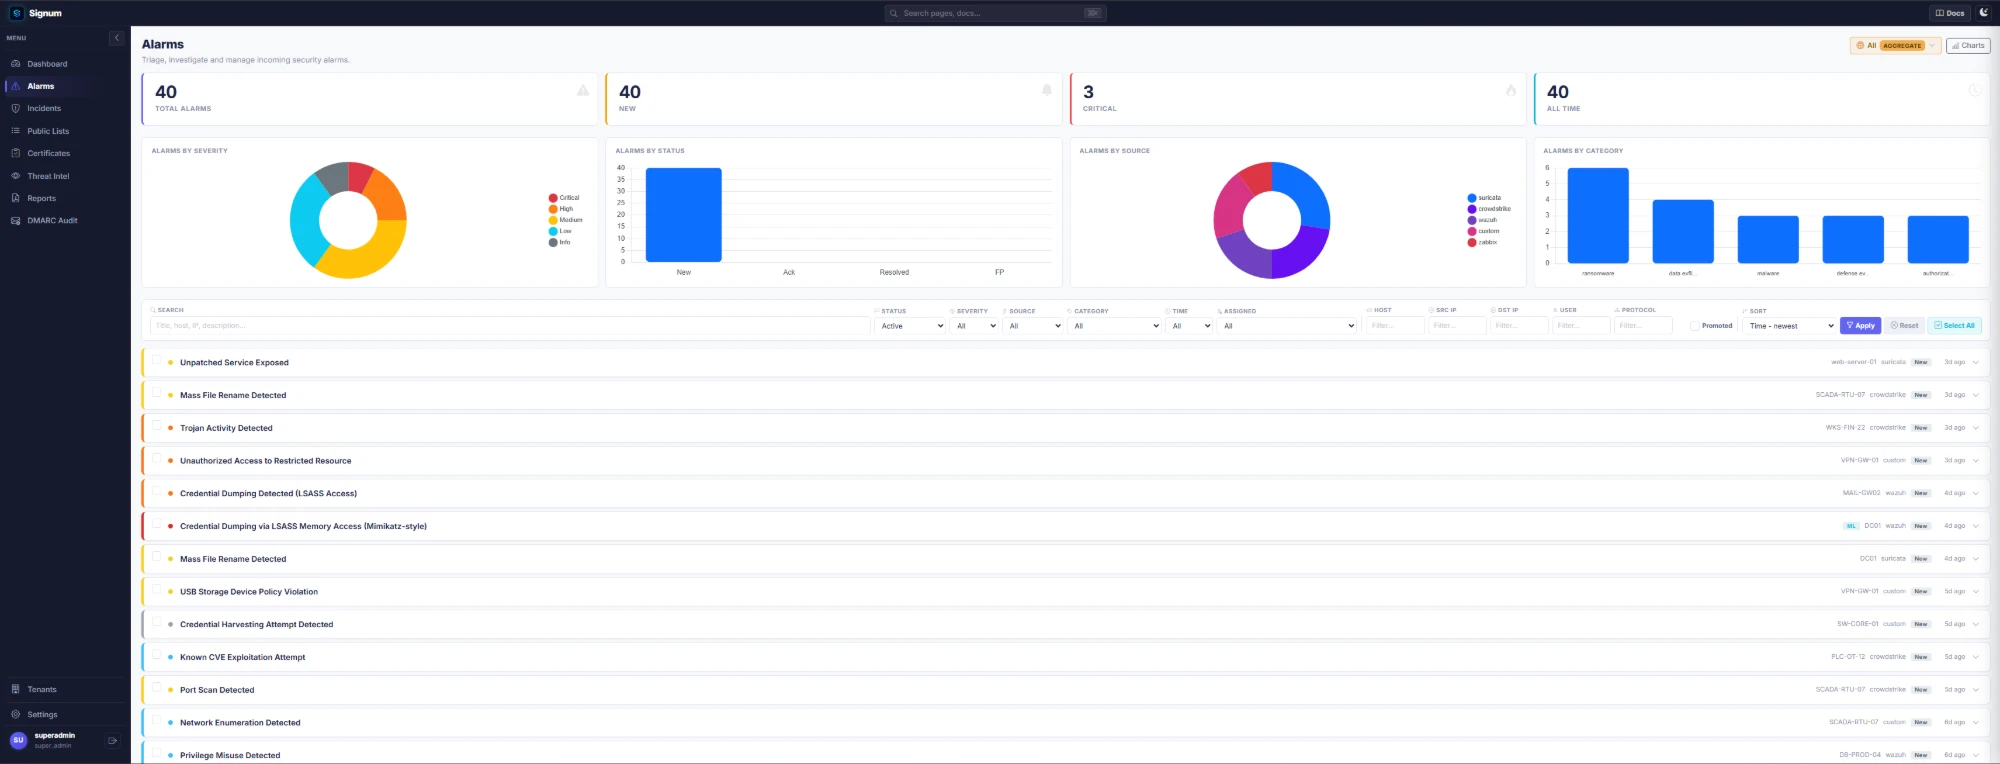
A queue built for triage

Filter by status, severity, source, category, host, IP or user, and sort the way you work. Charts show severity, status, source and category at a glance.

Signum alarm queue with severity, status and source charts
03

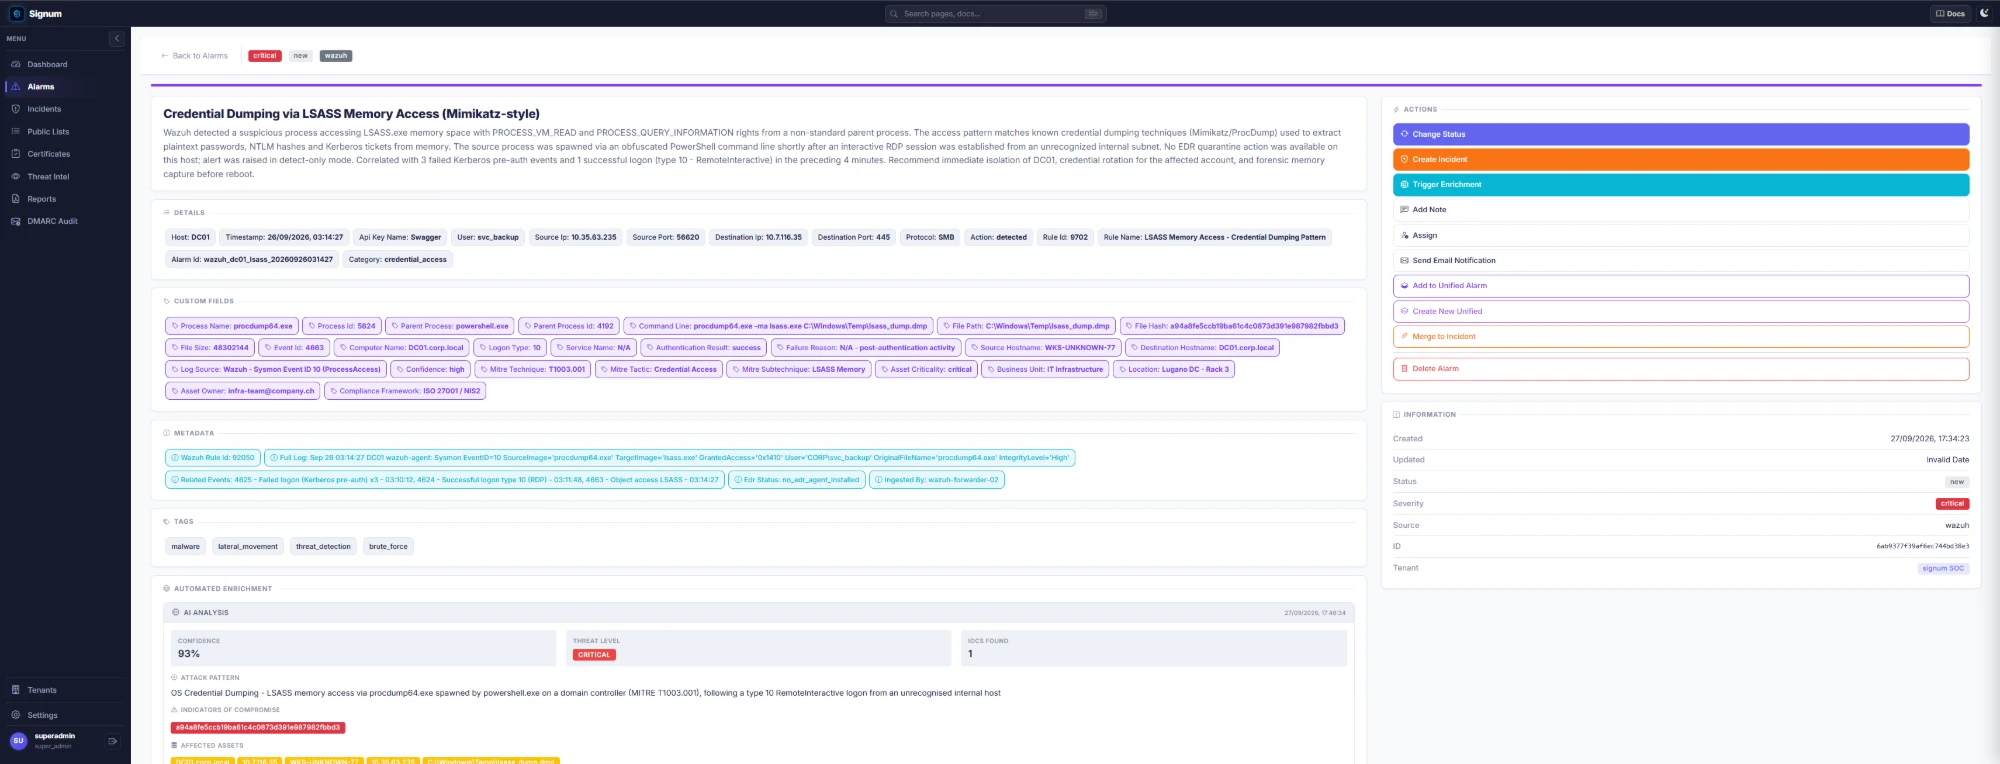
Everything about an alarm on one page

Details, custom fields, metadata and tags from the source, with the actions next to them: change status, create an incident, add a note, assign, or merge into a unified alarm.

Signum alarm detail page with details and custom fields
04

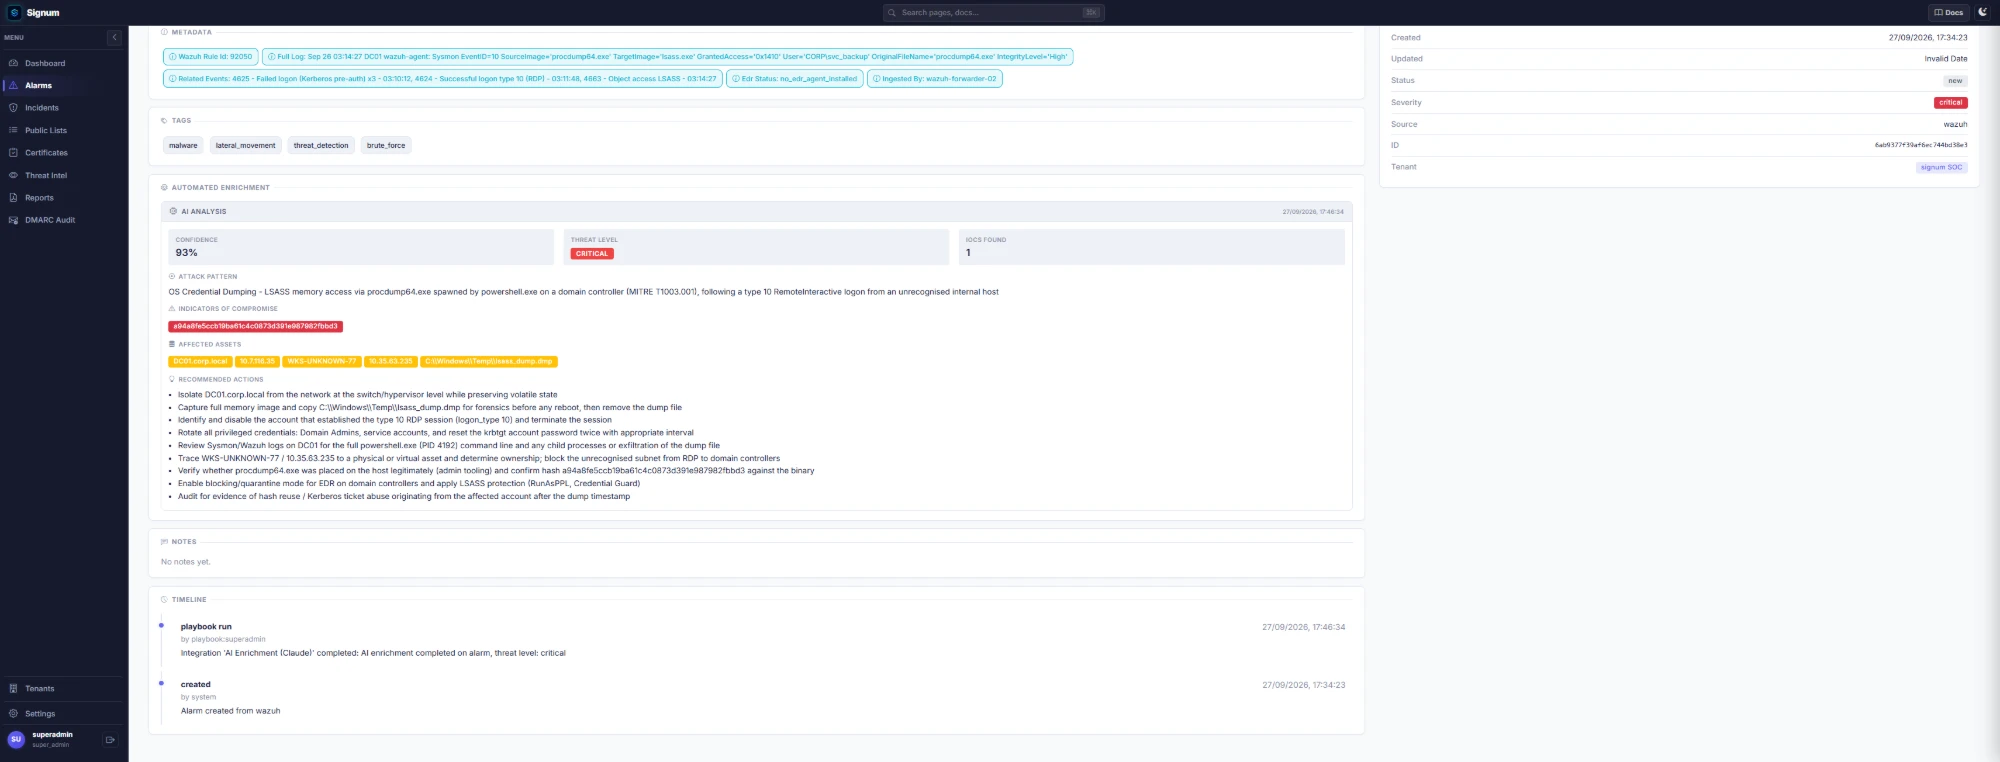
Enrichment that stays with the case

An analysis with threat level, confidence, indicators, affected assets and recommended actions, plus a timeline of everything that happened to the alarm.

Signum AI analysis with indicators and recommended actions
05

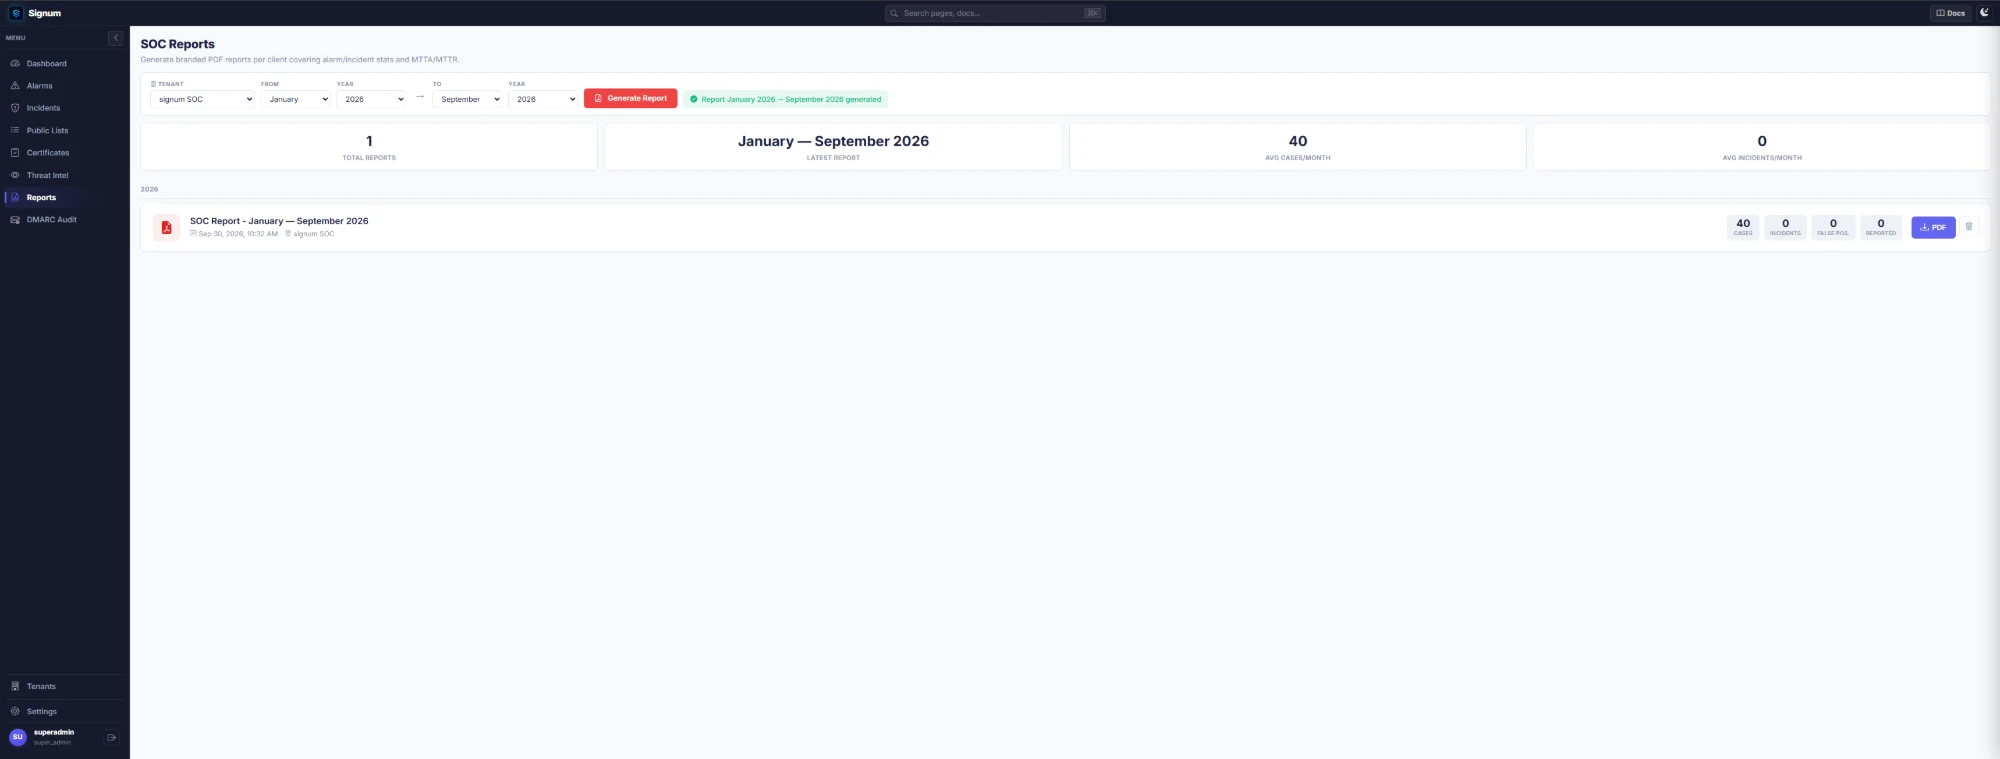
Reports ready to hand over

Pick a tenant and a period and generate a branded PDF with alarm and incident statistics and MTTA/MTTR.

Signum report generator with a generated PDF report
Why a platform

What changes on day one

Without SignumWith Signum
AlarmsEach tool and each customer has its own console to checkOne queue across every source and every customer
NoiseThe same event shows up a hundred timesRelated alerts fold into a single unified alarm
HandoverNotes live in chat threads and emailAssignment, status and history stay on the case
ResponseManual steps that differ from analyst to analystPlaybooks run the same steps every time
ReportingA monthly report assembled by handA PDF per tenant with MTTA, MTTR and timelines
AccessShared logins, or a separate tool per customerRoles per user, limited to the tenants they cover
The platform

From raw alert to closed incident

One workflow for the whole SOC lifecycle, designed for teams that look after several organizations at the same time.

Triage at scale

Alarms arrive in a common format: severities are mapped from whatever the source sends, duplicates are dropped by alarm id, and unified alarms fold a storm of related alerts into one item you can act on.

Respond with context

Promote an alarm to an incident and its whole history comes with it. Optional AI enrichment suggests a threat level and pulls out indicators; playbooks written in Python carry out the response.

Prove the work

Dashboards that show what is really open, a full audit trail, and per-tenant PDF reports (MTTA and MTTR, top sources, incident timelines) ready for the monthly review.

How it works

Five steps, one thread

Every alarm follows the same path, and every step is recorded against the tenant it belongs to.

  1. 1

    Collect

    Sources push alarms through the REST API or webhooks with a tenant-scoped key. Severities are normalized and repeats are dropped.

  2. 2

    Group

    Related alerts are folded into a unified alarm, so a hundred firewall events become one line in the queue.

  3. 3

    Triage

    Analysts assign, comment and look up IP and domain reputation without leaving the alarm.

  4. 4

    Respond

    Escalate to an incident, ask for an AI analysis if useful, and run a playbook to contain the problem.

  5. 5

    Close and report

    The closing status is pushed back to the source platform, and the month ends with a PDF report per tenant.

Capabilities

What is in the box

The day-to-day tools of an operations team, in a single self-hosted platform.

Unified alarms

Group related alerts into one entity with shared status, notes and timeline: triage hundreds as one.

Incident management

Status workflow, assignment, merge & promote, optimistic concurrency. No lost updates between analysts.

AI enrichment

AI-powered analysis on alarms and incidents: threat level, IOC extraction, similar incidents, next actions.

SOAR playbooks

Tenant-authored Python automations run in ephemeral, network-restricted containers: power without risk.

Auto status-sync

Close an incident and Signum pushes the status back to the originating platform, tickets included.

DMARC monitoring

Automatic aggregate-report collection straight from your report mailboxes, SPF/DKIM analytics per tenant.

Certificates & IP lists

TLS expiry monitoring and firewall-ready allow/block lists served as plain-text feeds your appliances pull.

Threat intelligence

One-click IP/domain reputation through your configured providers, cached and rate-limit aware.

The MSP foundation

Many organizations, one platform, no shared data

Tenant separation is not a filter added on top of the UI. It is enforced at the query layer on every read and every write, and it fails closed: if the tenant is unknown, nothing is returned.

  • Seven roles, from super admin to read-only viewer, with a permission check on every endpoint.
  • Cross-tenant analysts. Give an analyst exactly the organizations they cover and nothing more.
  • SSO per tenant with any OpenID Connect provider, verified token signatures and safe auto-provisioning.
  • Tenant-scoped API keys. An ingest key is pinned to its organization and cannot reach beyond it.
Optional AI enrichment

A second opinion, when you ask for it

On any alarm, unified group or incident an analyst can request an analysis. Signum sends the case context to the AI integration you configured and stores the structured answer next to the case. Nothing runs automatically and nothing is closed for you.

  • Structured answer with threat level, confidence, attack pattern, indicators, affected assets and suggested actions.
  • Stays with the case. The analysis follows the alarm when it is promoted to an incident.
  • Treated as untrusted input. The output is validated and shown escaped, never executed.
Security by design

Held to the standard we would ask of any vendor

A security tool sits in a privileged position, so it has to be the hardest thing on the network to abuse. These behaviors are covered by an automated test suite.

Identity and access

  • Default-deny API. Every endpoint requires a verified identity.
  • Hardened authentication. bcrypt, httpOnly cookies, brute-force lockout, instant session revocation.
  • Verified tokens and scoped keys. OIDC tokens are verified; API keys are tied to one tenant.

Data and tenancy

  • Isolation in the query layer. Enforced on every read and write, and it fails closed.
  • Data stays with you. Self-hosted, in your infrastructure.
  • Audit trail per tenant. Logins, changes and list edits, visible only to those allowed to read them.

Execution and network

  • Sandboxed playbooks. Non-root, throwaway containers with a read-only filesystem, no capabilities and an isolated network.
  • SSRF-guarded egress. Outbound requests built from user input are resolved and checked first.
  • AI output is untrusted. Validated, shown escaped, never executed.

Web application

  • Strict CSP. No inline script and no unsafe-inline, so injected markup has nothing to execute.
  • Verified by tests. These behaviors are covered by an automated test suite.
Deployment

It runs on your side of the firewall

Signum is self-hosted. Alarms, incidents, reports and credentials stay in your infrastructure, and the only outbound connections are the ones you configure yourself.

  • You own the data. It lives on your servers, under your backup and retention rules.
  • You choose the integrations. AI, threat intelligence and identity providers are all optional and configured by you.
  • You plug it in your way. Feeds for firewalls, a REST API for everything else.
Specifications

Signum at a glance

Deployment
Self-hosted, in your own infrastructure.
Tenancy
Multi-tenant. Isolation is enforced at the query layer on every read and write, and fails closed.
Identity
OpenID Connect SSO per tenant, plus local accounts with bcrypt hashing, brute-force lockout and instant session revocation.
Access control
Seven roles, from super admin to read-only viewer, with a permission check on every endpoint. Analysts can be granted several tenants.
Ingestion
REST API and webhooks with tenant-scoped keys. Severity normalization and deduplication by alarm id.
Sources
SIEM, EDR and XDR, NDR, network monitoring, perimeter and firewalls, email security, threat intelligence feeds, identity, ticketing and ITSM.
Automation
Tenant-authored Python playbooks in ephemeral, non-root containers with a restricted network.
AI enrichment
Optional and on demand, through the AI integration you configure. Output is validated and never executed.
Reporting
Branded PDF per tenant and period with alarm and incident statistics, MTTA and MTTR.
Monitoring
DMARC aggregate reports, TLS certificate expiry, allow and block IP lists served as plain-text feeds.
Audit
Per-tenant audit trail of logins, changes and list edits.
Questions

Things people usually ask

Something missing? Write to [email protected] and we will answer directly.

We are an MSP. How do we handle many customers?

Create one tenant per customer. Each tenant has its own alarms, users, integrations, playbooks and reports, and your analysts are granted only the tenants they cover. One person can work across all of them from a single queue.

Can our customers log in and see their own data?

Yes, if you want that. Give customer staff a read-only viewer role or a tenant admin role, and they see only their own organization. Single sign-on can be set up per tenant.

We are a single company. Is Signum still useful?

Yes. Run one tenant and you get the same queue, incidents, playbooks and reports. If you later add subsidiaries or business units, they become tenants of their own.

Does Signum replace our SIEM or EDR?

No. Those tools keep detecting. Signum receives what they raise and gives your analysts one place to triage, escalate and report.

Is it only available self-hosted?

Yes. Signum is deployed in your own infrastructure so that alarm data and credentials never leave your control. Get in touch to talk through sizing and requirements for your environment.

Do we have to use the AI features?

No. Enrichment is optional, runs only when an analyst asks for it, and uses the AI integration you configure. Without one, the rest of the platform works exactly the same.

How is one tenant kept apart from another?

Every query is scoped to the tenant on both reads and writes, and requests without a resolved tenant return nothing. API keys are bound to a single organization, and analysts only see the tenants they were granted.

What can a playbook do?

Playbooks are Python scripts written per tenant. Each run happens in a short-lived, non-root container with a read-only filesystem and a restricted network, so a faulty script cannot reach the rest of your systems.

Which single sign-on options are supported?

Any OpenID Connect identity provider, configured per tenant. Tokens are signature-verified and users can be provisioned automatically on first sign-in.

How do we get started?

Request a demo. We walk through Signum with your kind of sources and tenant layout, and agree the next steps from there.

See it with your own setup

A demo is a working session, not a slide deck: we look at your sources, your tenant structure and the playbooks you would want first.

[email protected]